Endpoint Detection and Response (EDR) Solution
A solution for in-depth behavioural monitoring of workstations and servers, detecting attacks through signs of anomalous behaviour rather than relying solely on known malware signatures.
Highlights
What sets it apart.
Continuous recording of process activity, files, network operations and configuration changes
Behaviour-based detection that can identify attack techniques for which no signature yet exists
Isolation of compromised machines from the network directly from the central management console
Trace data for reconstructing the entire attack chain after an incident
Overview
Endpoint Detection and Response (EDR) Solution
How it differs from antivirus software
Traditional antivirus software matches files against a list of known malware signatures — effective against common threats but powerless against custom-written attack tools. EDR takes a different approach: it observes behaviour on the machine and detects anomalous sequences of actions, even when each individual operation is legitimate.
Data recorded by EDR
- Which process launched which other process, and with what parameters
- Files that are created, modified or encrypted
- Outbound network connections and their destinations
- Changes to the registry, scheduled tasks and persistence mechanisms
Deployment notes
The EDR agent runs resident on every machine, so its impact on performance and its compatibility with operational software must be assessed. NST runs a pilot on a small group before rolling out across the entire organisation.
Specifications
Technical specifications.
- Supported operating systems
- To be updated
- Agent resource usage
- To be updated
- Detection mechanism
- To be updated
- Trace data retention period
- To be updated
- Remote response capabilities
- To be updated
- Deployment model
- To be updated
Detailed specifications are provided in the official technical documentation. Call +84 912 211 467 for the full version.
Use cases
Where it is deployed.
- Protecting staff workstations and critical operational servers
- Detecting targeted attacks that have bypassed traditional defences
- Investigating the scope of impact after a compromised machine is discovered
Same product group
Cyber operations
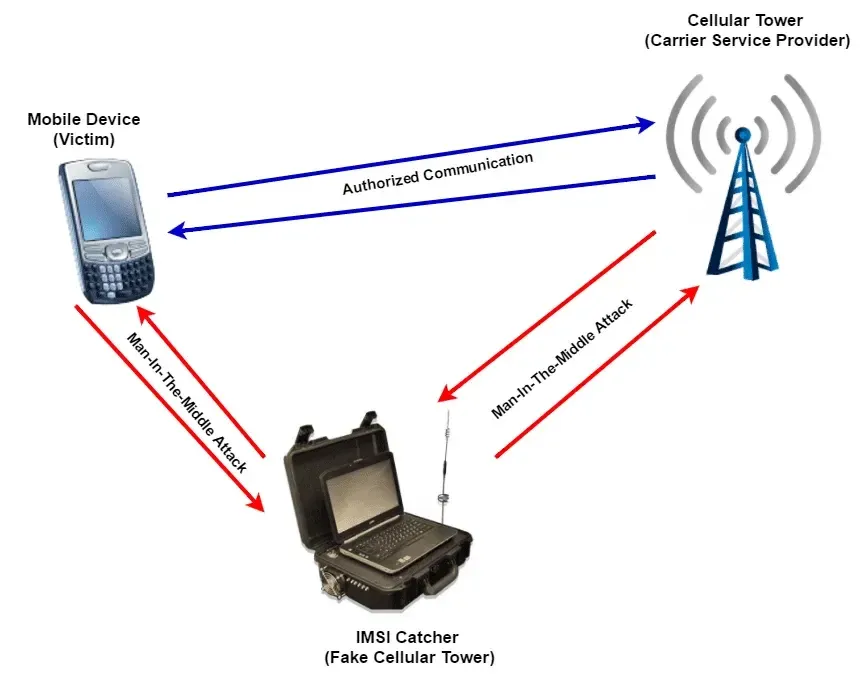
Mobile Network Monitoring System (IMSI)
A specialised solution for identifying and analysing mobile subscribers for criminal investigation and technical reconnaissance, operating within licensed areas.
View details
SMS Analysis System
A solution for signals intelligence collection and cybersecurity testing, supporting SMS protocol analysis and mobile network traffic monitoring for digital investigations.
View details
GSM / LTE / WiFi Signal Testing Equipment
A security testing system for network stress testing and quality assessment of telecommunications infrastructure, detecting protocol vulnerabilities before real-world deployment.
View detailsContact
Need a solution for your organisation?
NST’s engineering team is ready to discuss your operational requirements, integration approach and deployment conditions.