Security Information and Event Management (SIEM) System
A platform that collects, normalises and correlates logs from across the entire information system, turning millions of discrete events into a small number of alerts worth human review.
Highlights
What sets it apart.
Collects logs from network devices, servers, applications and security devices
Normalises data into a common format for cross-correlation between sources
Detection rules customised to the specific systems of each organisation
Log retention for post-incident investigation and compliance requirements
Overview
Security Information and Event Management (SIEM) System
The problem SIEM solves
Every device in a system keeps its own logs, in its own format. A real attack rarely leaves a complete trail on a single device — the traces are scattered across firewalls, authentication servers, workstations and applications. SIEM gathers these scattered fragments, normalises them into a common language, and then finds the connections between them.
What determines effectiveness
- Log source coverage — if a device does not send logs, SIEM cannot see it
- Quality of detection rules — default rules rarely suit the specifics of each system
- Handling of false alerts — a poorly configured SIEM generates so many alerts that the operations team can no longer tell genuine alerts apart
Deployment notes
Choosing log sources requires balancing coverage against storage costs. NST surveys the existing system architecture to set the order of priority for integrating data sources.
Specifications
Technical specifications.
- Supported log sources
- To be updated
- Event ingestion rate
- To be updated
- Retention period
- To be updated
- Correlation mechanism
- To be updated
- Deployment model
- To be updated
- Scalability
- To be updated
Detailed specifications are provided in the official technical documentation. Call +84 912 211 467 for the full version.
Use cases
Where it is deployed.
- Detecting attacks through traces left across multiple different systems
- Post-incident forensic investigation based on long-term log storage
- Meeting regulatory requirements for log recording and retention
Same product group
Cyber operations
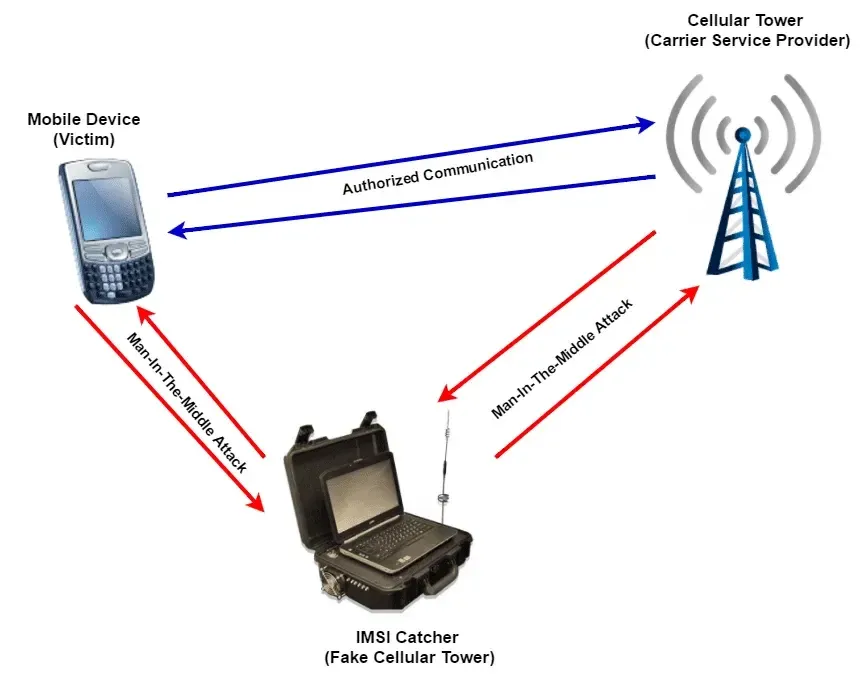
Mobile Network Monitoring System (IMSI)
A specialised solution for identifying and analysing mobile subscribers for criminal investigation and technical reconnaissance, operating within licensed areas.
View details
SMS Analysis System
A solution for signals intelligence collection and cybersecurity testing, supporting SMS protocol analysis and mobile network traffic monitoring for digital investigations.
View details
GSM / LTE / WiFi Signal Testing Equipment
A security testing system for network stress testing and quality assessment of telecommunications infrastructure, detecting protocol vulnerabilities before real-world deployment.
View detailsContact
Need a solution for your organisation?
NST’s engineering team is ready to discuss your operational requirements, integration approach and deployment conditions.