Incident Response Automation Platform (SOAR)
A platform that turns repetitive incident-handling steps into automated playbooks, shortening the time from detection to containment.
Highlights
What sets it apart.
Automated response playbooks for common types of incident
Connects to and controls existing security systems through programming interfaces
Incident lifecycle management: intake, assignment, handling, closure and review
Full logging of actions for review and process improvement
Overview
Incident Response Automation Platform (SOAR)
Why automation is needed
Most of a cybersecurity analyst’s time is spent on repetitive tasks: looking up IP addresses, checking against malware lists, collecting related logs, notifying the parties involved. Machines do these tasks faster than people, without missing anything. SOAR frees analysts to focus on the work that requires judgement.
The limits of automation
Not every decision should be handed to a machine. The practical principle:
- Fully automated — data collection and information enrichment steps, which have no impact
- Automated with approval — containment actions that affect users
- Kept for people — decisions involving critical operational systems
Deployment notes
SOAR only delivers results once incident-handling procedures have been standardised. NST helps review and standardise procedures before encoding them as automated playbooks.
Specifications
Technical specifications.
- Number of pre-built playbooks
- To be updated
- Supported integrations
- To be updated
- Playbook building method
- To be updated
- Deployment model
- To be updated
- Permission management
- To be updated
Detailed specifications are provided in the official technical documentation. Call +84 912 211 467 for the full version.
Use cases
Where it is deployed.
- Automatically isolating malware-infected workstations as soon as they are detected
- Automatically gathering supporting data to shorten analysts' analysis time
- Standardising incident-handling procedures across different shifts
Same product group
Cyber operations
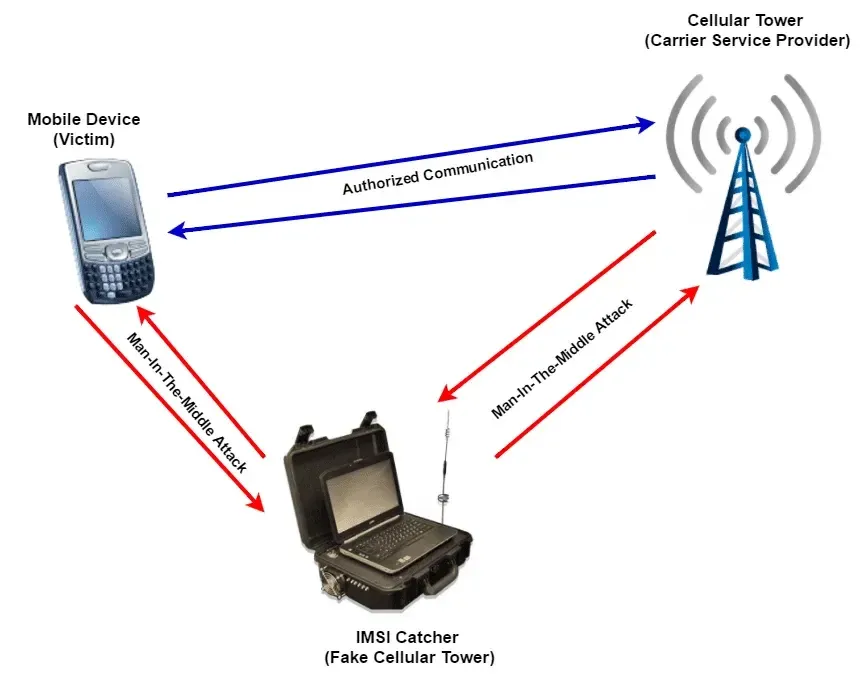
Mobile Network Monitoring System (IMSI)
A specialised solution for identifying and analysing mobile subscribers for criminal investigation and technical reconnaissance, operating within licensed areas.
View details
SMS Analysis System
A solution for signals intelligence collection and cybersecurity testing, supporting SMS protocol analysis and mobile network traffic monitoring for digital investigations.
View details
GSM / LTE / WiFi Signal Testing Equipment
A security testing system for network stress testing and quality assessment of telecommunications infrastructure, detecting protocol vulnerabilities before real-world deployment.
View detailsContact
Need a solution for your organisation?
NST’s engineering team is ready to discuss your operational requirements, integration approach and deployment conditions.