Security Operations Centre (SOC)
A continuously operating centre for information security monitoring and incident response, unifying people, processes and technology into a single defensive capability.
Highlights
What sets it apart.
Continuous monitoring of the entire information system, detecting signs of attack in real time
Procedures for receiving, triaging and handling incidents by severity level
Consolidates data from SIEM, EDR and other alert sources on a single operations screen
Periodic reports for management and for compliance with information security regulations
Overview
Security Operations Centre (SOC)
A SOC is a capability, not a product
A security operations centre can only function when all three components are in place: a trained team of analysts, clear incident-handling procedures, and a technology platform powerful enough to collect — correlate — automate. If any one of these components is missing, the others cannot be effective.
Constituent layers
- Centralised collection and analysis (SIEM) — gathers logs from across the system and detects anomalies through correlation rules
- Response automation (SOAR) — turns repetitive handling steps into automated playbooks
- Endpoint monitoring (EDR) — in-depth observation of behaviour on workstations and servers
- Operating procedures — incident classification, reporting lines, response playbooks
Build roadmap
NST deploys in phases rather than building everything at once: starting with visibility (complete log collection), moving on to detection (correlation rules suited to the specific system), and only then to automated response. This approach gives the organisation usable results from the very first phase.
Specifications
Technical specifications.
- Deployment model
- To be updated
- Operating mode
- To be updated
- Event processing capacity
- To be updated
- Core technology platform
- To be updated
- Standards compliance level
- To be updated
- Response time commitment
- To be updated
Detailed specifications are provided in the official technical documentation. Call +84 912 211 467 for the full version.
Use cases
Where it is deployed.
- Building in-house SOCs for agencies and organisations with critical information systems
- Upgrading existing information security monitoring capabilities to a continuous operations model
- Meeting the requirements for information system security assurance by classification level
Same product group
Cyber operations
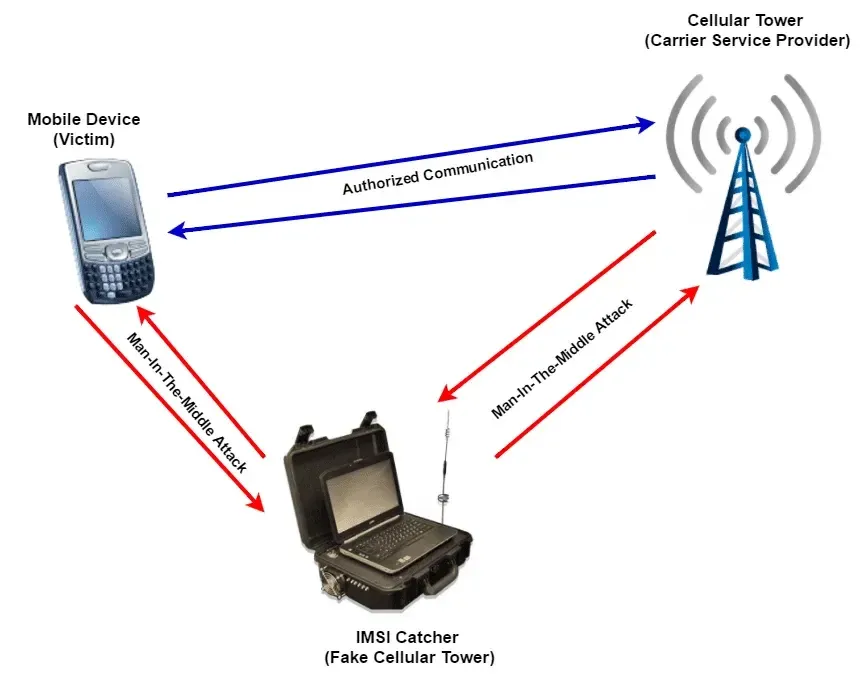
Mobile Network Monitoring System (IMSI)
A specialised solution for identifying and analysing mobile subscribers for criminal investigation and technical reconnaissance, operating within licensed areas.
View details
SMS Analysis System
A solution for signals intelligence collection and cybersecurity testing, supporting SMS protocol analysis and mobile network traffic monitoring for digital investigations.
View details
GSM / LTE / WiFi Signal Testing Equipment
A security testing system for network stress testing and quality assessment of telecommunications infrastructure, detecting protocol vulnerabilities before real-world deployment.
View detailsContact
Need a solution for your organisation?
NST’s engineering team is ready to discuss your operational requirements, integration approach and deployment conditions.